
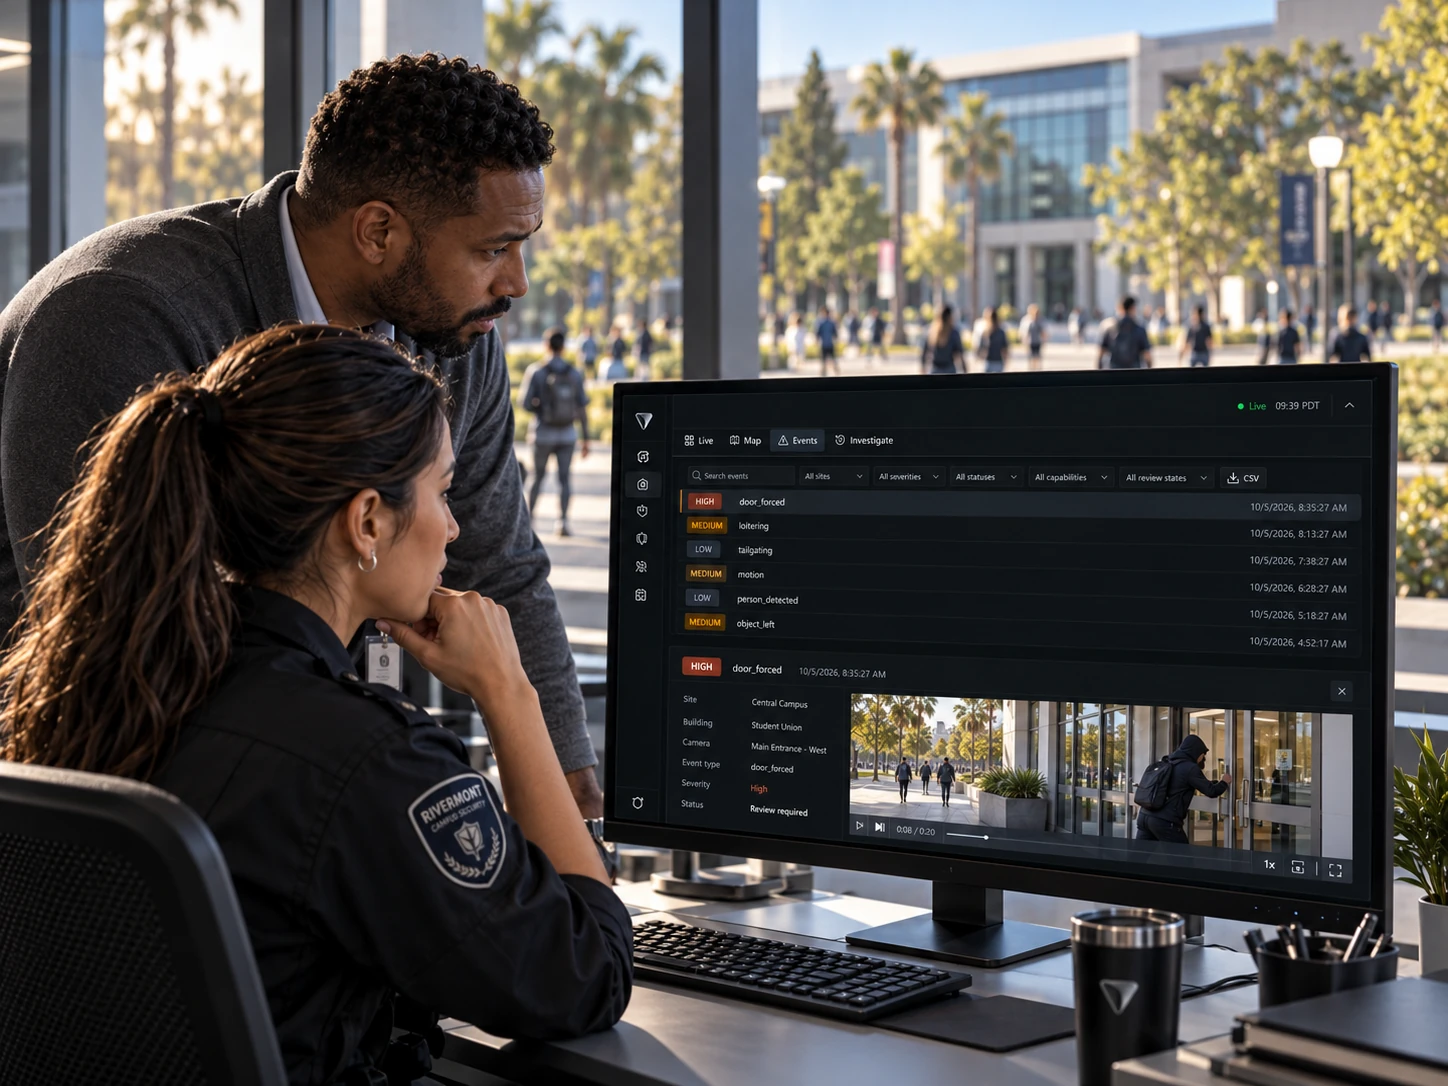
Events that arrive with a place attached, and a review step before they become someone's problem.
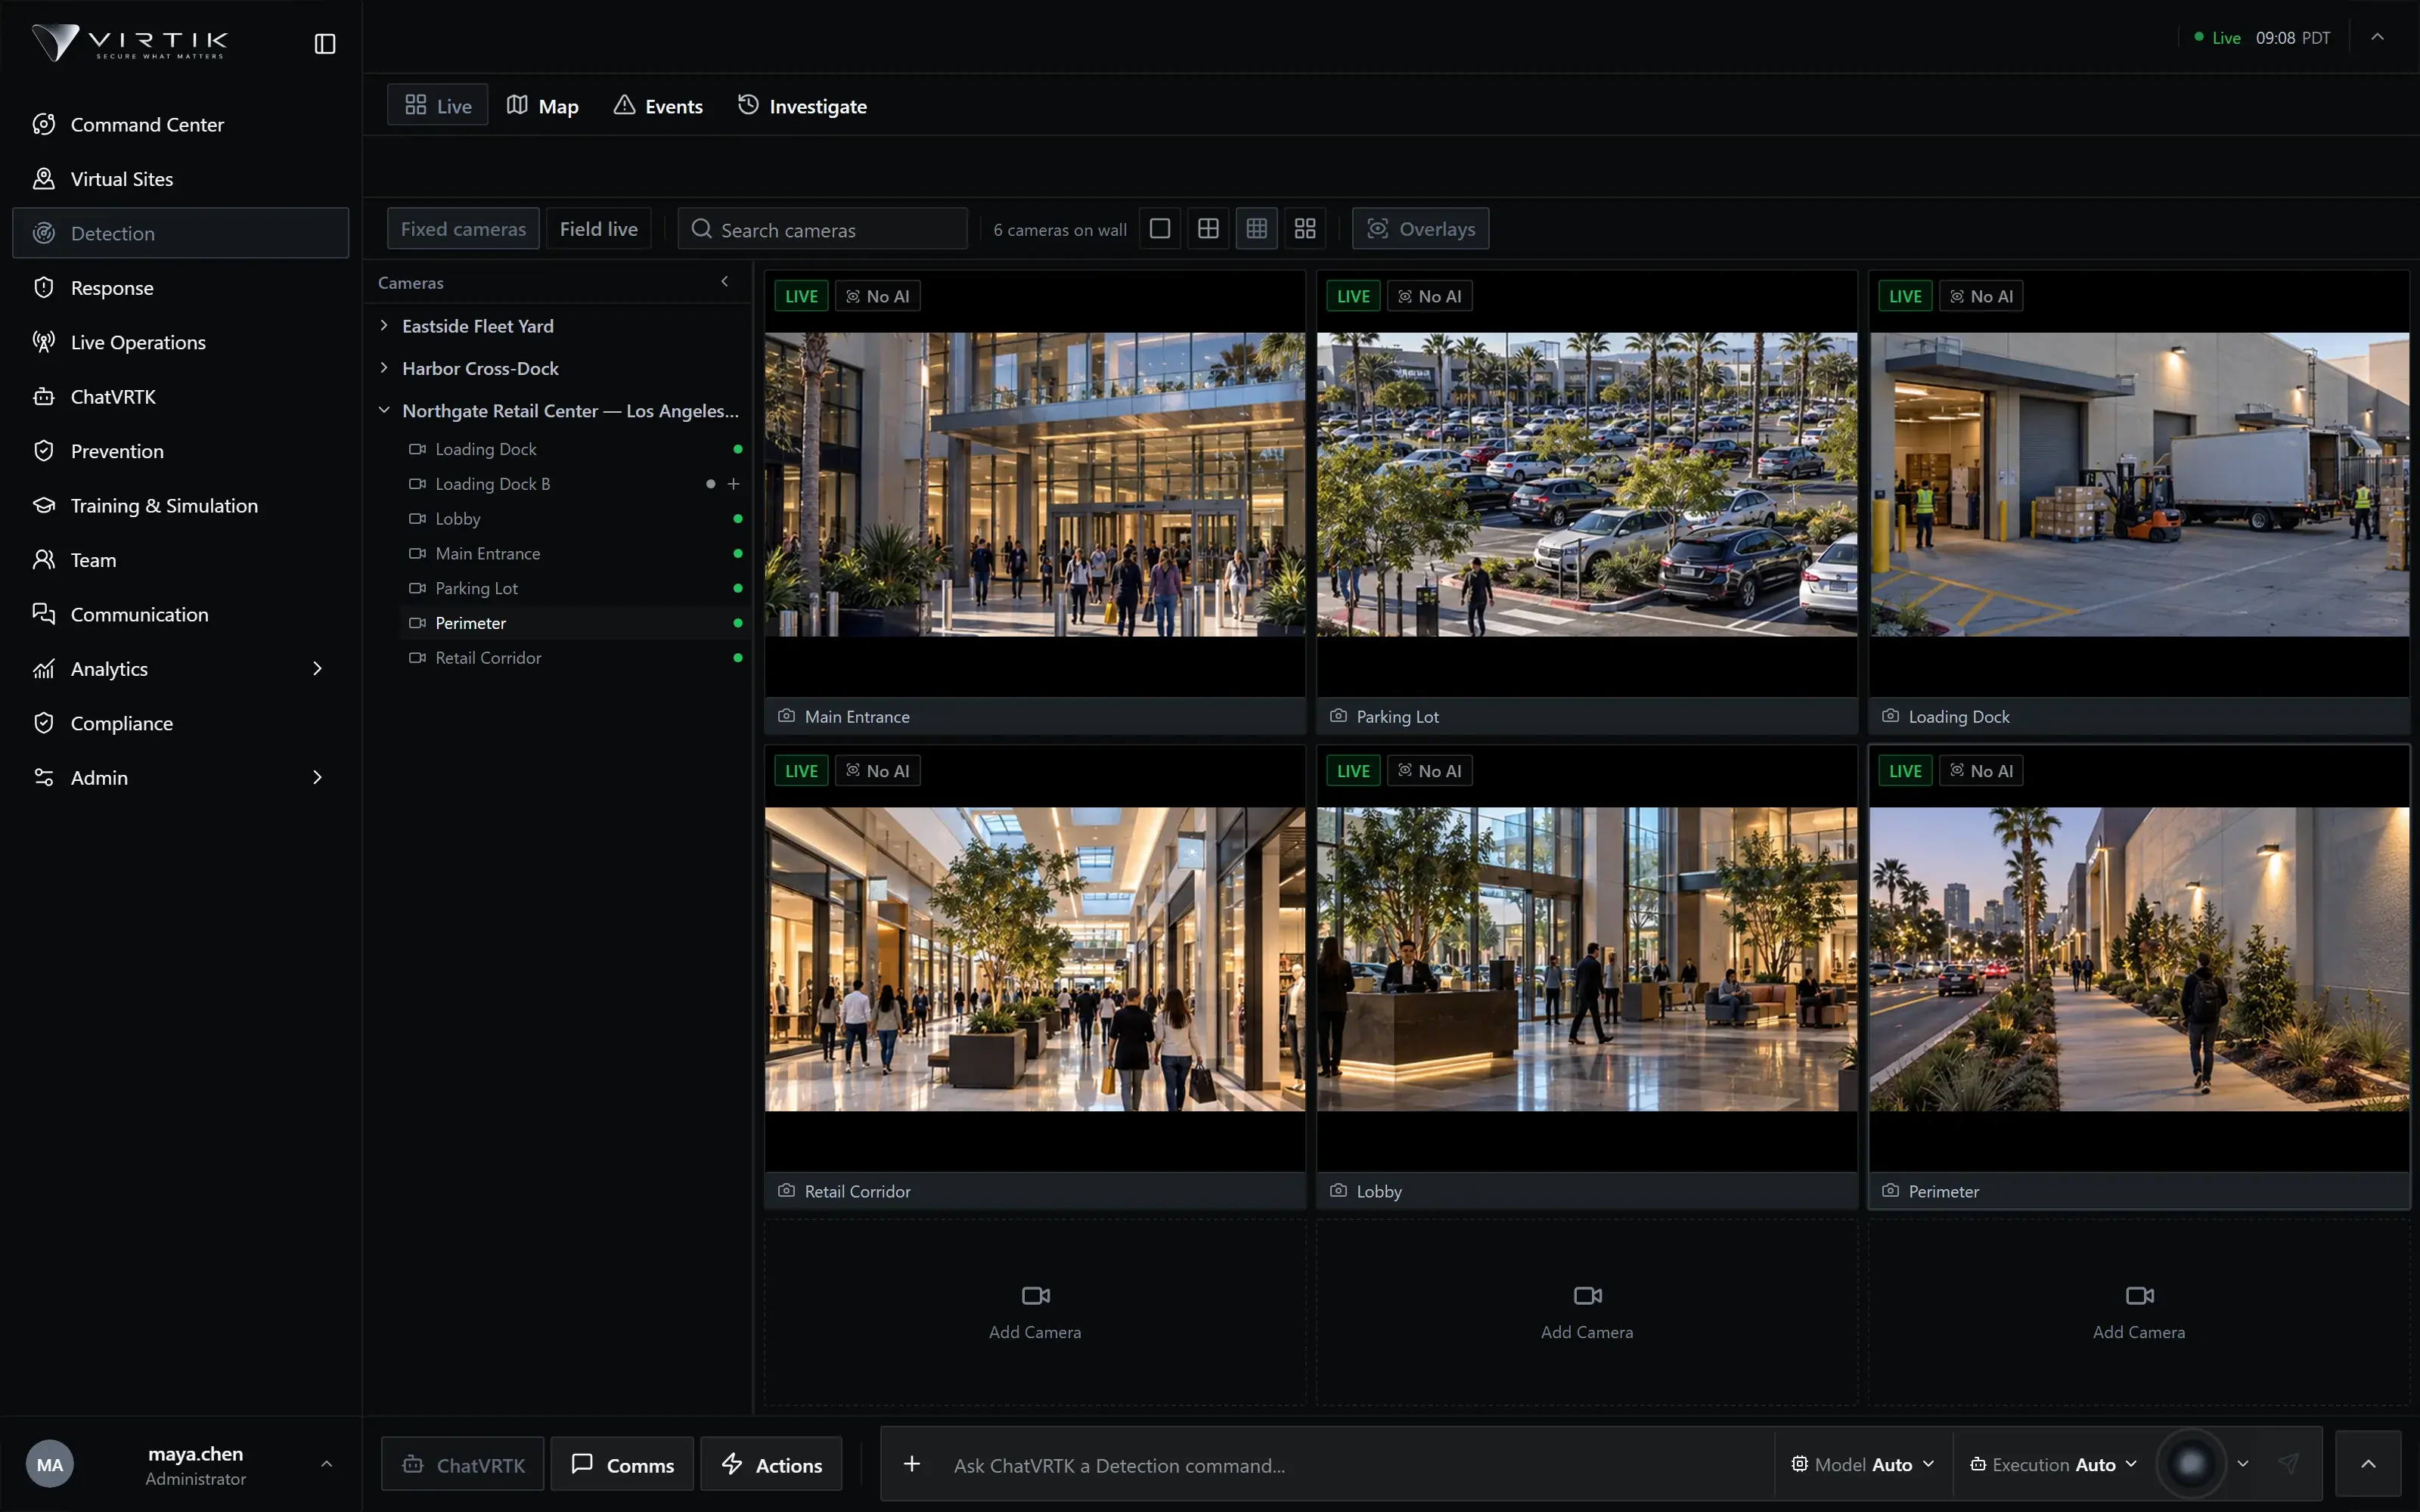
Camera and sensor ingestion that turns raw events into reviewable events an operator can escalate to incidents.
The problem
What goes wrong without it
An alert that cannot say which door, which floor or which zone forces a second investigation before anyone can respond to the first. Volume then trains operators to ignore the feed.
Detection ingests from cameras and sensors, resolves each event against the site model, and promotes it into an incident only through an explicit review step. What reaches an operator is something with a location and a reason to exist.
Capabilities
What Detection does
Described from the current product build. Availability can depend on your deployment and plan.
- Camera and sensor ingestion with rate limiting
- Events resolved against the site model rather than reported as bare coordinates
- Explicit review step between raw event and incident
- Escalation into the incident record Response works from
- Reviewable history rather than a stream that scrolls away
- Zero-state handling so a new tenant sees an honest empty state, not fabricated activity
Operational workflow
How it is used
These are ordered stages of real use, not a feature list rearranged.
- 01Ingest
Events arrive from cameras and sensors, rate-limited at the boundary.
- 02Resolve
Each event is located within the site graph.
- 03Review
An operator confirms, dismisses or escalates.
- 04Escalate
Confirmed events become incidents, carrying their evidence.
Operating it
Integration, security and deployment
Integrations
- ONVIF and RTSP camera systems
- Access control event sources
- Environmental and equipment sensors
- Signed webhooks for integration events (incident and detection events are not delivered yet)
Security & permissions
Ingestion endpoints are authenticated and rate-limited per tenant. Detections are tenant-isolated at the data layer, and reviewing or escalating is gated by operational role, so ingestion access never implies incident authority.
Security modelDeployment
- Cameras must be reachable and credentialed per organisation
- Site model should exist first, so detections can resolve to zones
- Ingestion volume shapes the connector tier required
Documentation
Where the detail lives
Documentation for this module is being prepared against the product. It is not published yet.
We publish documentation only once it has been checked against the product, rather than listing procedures nobody has run. The documentation home shows what is written, in review or planned.
Documentation homeRelated
Modules that share this model
These read from the same sites, personnel and incidents.
See Detection against your own sites
A working session using your operational context rather than a scripted tour. If your operation fits a plan available online, we will say so rather than route you through a sales process.